Every SOC analyst knows the feeling—alerts just keep coming, and it’s easy to lose track of what’s actually important. This constant noise isn’t just annoying; it can lead to real problems, like missing true threats or burning out your best people. AI log analysis tools promise to help by sorting through the chaos, but how do they actually make a difference? Let’s look at how these tools can cut down on alert fatigue and help security teams focus on what matters.
Table of Contents
- Understanding The Roots Of Alert Fatigue
- The Operational And Business Repercussions
- Leveraging AI For Smarter Alert Triage
- AI-Driven Detection And Behavioral Analytics
- Phased Implementation Of AI Log Analysis
- AI Frameworks For Enhanced Prioritization
- The Role Of AI In Reducing Log Ingestion Costs
- AI Log Analysis And Regulatory Compliance
- Case Studies In Alert Fatigue Impact
- Measuring And Quantifying Alert Fatigue
- The Future Of Security Operations With AI
- Moving Forward: Taming the Alert Beast
- Frequently Asked Questions
Key Takeaways
- Alert fatigue happens when teams are overwhelmed by too many notifications, especially false positives and duplicate alerts.
- AI log analysis tools can group related alerts, making it easier to spot real threats and ignore the noise.
- Automating the first steps of alert triage frees up analysts to focus on bigger problems and reduces burnout.
- Filtering out irrelevant logs before they’re stored not only cuts costs but also keeps the alert stream manageable.
- Tracking metrics like false positive rates and uninvestigated alerts helps teams see where improvements are needed and measure progress.
Understanding The Roots Of Alert Fatigue
Security teams everywhere know one thing too well: alert fatigue creeps up fast and doesn’t let go. It comes from constant waves of alerts flooding security tools, making it harder for analysts to spot something truly dangerous. If you can’t trust that an alert really means something is wrong, you start tuning everything out — and that’s when big threats slip through. While the initial problem seems technical, the real roots are much deeper and messier.
The Impact Of Overwhelming Notification Volumes
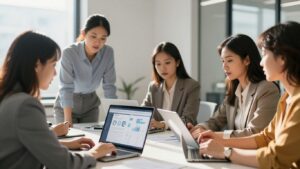
There’s no getting around the numbers — most organizations receive thousands of alerts every day, and a big chunk of them go unchecked. Here’s a quick overview:
| Metric | Value |
|---|---|
| Average daily security alerts per org | 2,992 |
| Unaddressed alerts (% of total) | 63% |
| Security teams citing alert fatigue | 76% |
The pileup isn’t just in the volume, but in how quickly these alerts stack on top of each other. It’s exhausting and kills focus before lunch. Over time, this crush of notifications pushes even the best analysts to start missing genuine problems, not just the background noise. Sometimes, it feels like no one is winning when everything is urgent.
Even if alert volumes go down a bit year over year, the issue sticks around because the signal buried in all the mess rarely improves at the same rate.
False Positives And Low-Fidelity Alerts
The heart of the issue is that many alerts don’t actually point to real danger. When a security tool raises a flag for something routine — like a network scan from a trusted system or a harmless software update — analysts waste time double-checking things that don’t matter. Some key facts:
- Nearly half of all alerts are false positives or lack enough detail to be useful.
- Some rule sets have barely changed in years, causing them to catch all the wrong things over and over.
- Alert storms can pop up from single incidents, burying important warnings in a sea of harmless noise.
A wave of unhelpful notifications not only clogs the workflow, but also trains teams to ignore the very system they’re supposed to rely on. The constant barrage leads to missed critical issues and eventually, analysts just stop caring.
Fragmented Tooling And Console Sprawl
No one loves flipping between ten different screens all day, yet that’s what modern security teams are stuck with. Each security platform has its own style, severity ratings, and even unique alert language. Some challenges that come with tool sprawl include:
- Analysts must learn and remember quirks of each tool’s alert logic.
- Related alerts about the same incident hit separate dashboards, never getting connected.
- Metrics and severity ratings aren’t standardized, so prioritizing becomes guesswork.
This fragmentation makes every investigation harder than needed. Important context falls through the cracks, and analysts start cherry-picking alerts that seem easy to handle just to clear the board.
The bottom line is: until you tackle the roots of alert fatigue — overwhelming alert volume, bad signal quality, and console overload — the risk of missing the real threat will always stick around.
The Operational And Business Repercussions
When security teams get swamped with alerts, it’s not just an IT problem; it spills over into the whole business. Think about it: if your analysts are drowning in notifications, they can’t possibly catch everything. This leads to some pretty serious fallout.
Analyst Burnout And Talent Retention Challenges
It’s no secret that security analysts are feeling the heat. Constantly sifting through mountains of alerts, many of which turn out to be nothing, is exhausting. This relentless pressure leads to burnout, making it tough to keep good people. Reports show a significant percentage of analysts experience burnout, and many junior folks leave the field within a few years. Losing experienced analysts means losing valuable knowledge and slowing down response times. It’s a vicious cycle that impacts team morale and operational effectiveness.
Delayed Detection And Increased Breach Impact
When alerts pile up, real threats can get buried. Analysts might miss critical indicators because they’re busy with low-priority noise. This delay in detecting a genuine intrusion means attackers have more time to move around, steal data, or cause damage. The longer it takes to spot a breach, the worse the consequences. We’re talking about potentially larger data exfiltration, more widespread system compromise, and a much harder recovery process. For instance, a missed alert about unusual user activity could be the first sign of an insider threat, which can be incredibly damaging and costly IBM Cloud Pak for Integration AI Agents.
Reputational Harm And Financial Damage
Ultimately, alert fatigue can lead to major business problems. A significant data breach, especially one that could have been caught earlier, can severely damage a company’s reputation. Customers lose trust, partners get nervous, and the brand image takes a hit. Financially, the costs are staggering. Beyond the direct expenses of incident response and recovery, there are regulatory fines, legal fees, and lost business. The average cost of a data breach is millions of dollars, and that number keeps climbing. Ignoring the signal in the noise isn’t just an operational hiccup; it’s a direct threat to the bottom line and the company’s standing in the market.
Leveraging AI For Smarter Alert Triage
Okay, so we’ve talked about how overwhelming alert volumes can really mess with your security team. But what if we could actually make those alerts work for us, instead of against us? That’s where AI comes in, and it’s not just some futuristic dream anymore. It’s about making sense of the chaos.
Intelligent Alert Correlation Across Tools
Think about it: your security tools are probably spitting out alerts from every angle – your firewall, your endpoint detection, your cloud logs. Individually, they might seem like minor blips. But AI can look at all these scattered signals and see the bigger picture. It connects the dots between events that happen across different systems and over time. Instead of getting a hundred separate notifications about a suspicious login, a file download, and a network anomaly, AI can group them together into one coherent incident. This means analysts spend less time hunting for related events and more time understanding the actual threat. It’s like having a detective who can instantly piece together clues from multiple crime scenes.
Context-Aware Risk Prioritization Engines
Not all alerts are created equal, right? Some are critical, and some are just noise. AI-powered systems can figure out which alerts actually matter by looking at a bunch of context. This includes things like:
- How sensitive is the system or data involved?
- What’s the role and usual behavior of the user who triggered the alert?
- Does this alert match any known bad actor activity from threat intelligence feeds?
- What has this system or user done in the past?
By considering these factors, AI can assign a risk score to each alert. This helps your team focus on the most pressing issues first, rather than getting bogged down by low-priority warnings. It’s about making sure the most important fires get put out before the small ones even start to smolder. This kind of smart prioritization is key to avoiding burnout and keeping your security posture strong. For example, an alert about a critical server showing unusual activity would be flagged much higher than a similar alert on a non-essential workstation. This helps teams at Zenduty manage their incident response more effectively.
Automated Triage For Tier 1 Investigations
This is where AI really shines for reducing that alert fatigue. A huge chunk of the alerts security teams deal with are what we call ‘Tier 1’ – the routine, often repetitive investigations. AI can actually handle a lot of this automatically. It can perform initial checks, gather relevant data, and even rule out common false positives. Studies suggest AI can automate over 95% of these Tier 1 investigations. This frees up your human analysts to tackle the really complex, high-stakes incidents that require human judgment and creativity. It’s not about replacing analysts, but about giving them back their time and mental energy to do the work that truly needs their skills. Imagine your team spending their days on challenging investigations instead of sifting through mountains of low-level alerts. That’s the goal here.
AI-Driven Detection And Behavioral Analytics
Traditional security tools often rely on known signatures to spot threats. It’s like having a list of known bad guys and only looking for them. But what about the new guys, or the ones who are really good at blending in? That’s where AI-driven detection and behavioral analytics come in. Instead of just looking for signatures, these systems learn what ‘normal’ looks like for your users, your servers, and your network. Then, they flag anything that seems out of the ordinary.
Replacing Signature-Heavy Rules With Behavior-Based Detection
Think about it: signature-based detection is always playing catch-up. Attackers are constantly changing their tactics, so security teams have to constantly update their rules. It’s a never-ending game. Behavioral analytics, on the other hand, focuses on the actions an entity takes. If a user account suddenly starts accessing sensitive files it never touched before, or if a server starts communicating with suspicious external IP addresses, that’s a red flag, regardless of whether a specific signature exists for that activity. This approach is much better at catching novel threats. It shifts the focus from identifying known bad actors to spotting unusual behavior that could indicate a compromise.
Detecting Advanced And Insider Threats
This is where AI really shines. It can spot subtle deviations that a human analyst might miss, especially when buried under a mountain of alerts. For instance, detecting insider threats is notoriously difficult because the actions might look legitimate on the surface. However, AI can build a baseline of normal behavior for each user and flag anomalies, like unusual access patterns or data exfiltration attempts, even if they don’t match any known malware signature. It’s also great for spotting advanced, multi-stage attacks that unfold over time across different systems. The ability to understand normal user and system behavior is key here.
Reducing Alert Noise Through Signal Clarity
One of the biggest complaints from security teams is the sheer volume of alerts, many of which turn out to be false positives. AI helps cut through this noise. By understanding context and baselining normal activity, AI can filter out a lot of the low-priority or irrelevant events before they even become alerts. This means analysts spend less time sifting through junk and more time investigating genuine threats. It’s about making sure the alerts that do reach the analysts are high-fidelity and actionable. This leads to:
- Fewer false positives cluttering the queue.
- Faster identification of real security incidents.
- Improved analyst focus and reduced burnout.
The goal isn’t just to detect more things, but to detect the right things more effectively. By understanding the normal patterns within your environment, AI can highlight deviations that truly matter, making your security operations more efficient and less overwhelming.
Phased Implementation Of AI Log Analysis
So, you’ve decided to bring AI into your log analysis process to tackle that pesky alert fatigue. That’s a smart move, but jumping in headfirst without a plan can be, well, messy. Think of it like renovating a house; you don’t just start tearing down walls. You need a strategy, a phased approach to make sure everything works together and you don’t end up with more problems than you started with. The goal here is to gradually integrate AI, making sure each step builds on the last, leading to a more efficient and less noisy security operations center.
Quick Wins: Rule Tuning And Threshold Adjustments
Before you even think about complex AI models, let’s talk about the low-hanging fruit. Often, a big chunk of alert fatigue comes from poorly configured rules and thresholds in your existing systems. This is where you can get some immediate relief. Start by reviewing your current alert rules. Are they still relevant? Are they too sensitive? You might find that many alerts are triggered by normal, everyday activity that just happens to trip a specific rule. Tuning these rules, perhaps by adding more specific conditions or adjusting the sensitivity thresholds, can significantly cut down on the noise. It’s about making your current tools smarter before adding new ones. This is a great place to start because the impact is often immediate and doesn’t require a massive overhaul. You can also look at basic automation for these adjustments, like setting up automated alerts for rules that consistently generate false positives, prompting a review.
Structural Changes: Alert Enrichment And Feedback Loops
Once you’ve cleaned up the obvious noise, it’s time to think about adding more context. This is where AI starts to play a more direct role, not by replacing your current systems, but by making them better. Alert enrichment means automatically adding more information to an alert when it fires. Instead of just seeing an IP address, the enriched alert might include geolocation data, known threat intelligence about that IP, and details about the user or system involved. This extra context helps your analysts understand the severity and potential impact of an alert much faster, reducing the time spent on manual investigation. Building a feedback loop is also key here. When an analyst investigates an alert, they should be able to easily provide feedback on whether it was a true positive, a false positive, or something else. This feedback is gold for AI systems; it helps them learn and improve their accuracy over time. This iterative process is how you build trust in the system and make it more effective. For example, you might implement a system where analysts can tag alerts, and this data is fed back into the AI model to refine its understanding of your specific environment. This is a core part of strategic AI adoption.
Strategic Transformation: AI Triage And Automation
This is the big leagues, where AI takes on more significant responsibilities. After tuning rules and implementing enrichment, you can start using AI for automated triage. This means the AI system can analyze incoming alerts, correlate them with other events, assess their risk based on the enriched context, and then decide on the next steps. For low-priority or clearly false positive alerts, the AI might automatically close them. For medium-priority alerts, it could assign them to the right team or gather more information. Only high-priority, high-confidence alerts would be escalated directly to human analysts. This frees up your analysts to focus on the most critical threats, rather than sifting through mountains of less important notifications. This level of automation requires a solid foundation, built on the previous phases. It’s about moving from a system where humans are constantly reacting to alerts, to one where AI handles much of the initial processing, allowing your team to be more proactive. This transformation is about making your security operations more intelligent and adaptable, which is vital in today’s threat landscape. The ultimate aim is to create a security posture that can adapt to new threats, much like how AI is being used to optimize project workflows.
AI Frameworks For Enhanced Prioritization
So, how do we actually make sense of all these alerts without losing our minds? That’s where AI frameworks come into play. Think of them as smart assistants for your security team, helping to sort the truly important stuff from the background noise. It’s not just about having more alerts, but about having better alerts that tell you something meaningful.
Machine Learning For Alert Actionability Scoring
One of the biggest headaches is figuring out which alert actually needs someone to jump on it right away. Machine learning models can help here by scoring alerts based on how actionable they are. This means the system looks at things like how sensitive the affected asset is, who the user is, and if there’s any threat intelligence pointing to this being a real problem. It’s about giving a priority score that reflects the actual risk to the business. A study showed a model that could cut down response times for real incidents and also get rid of a good chunk of those annoying false positives, all while still catching most of the actual threats. Pretty neat, right?
Retrieval-Augmented Generation For Contextual Data
Now, imagine an alert pops up. What’s the first thing you’d want to know? Probably some background info, right? Retrieval-Augmented Generation, or RAG, is a fancy way of saying the AI can go fetch relevant data from other sources to give you more context. For example, it could pull in information about agreed-upon performance limits from your service level agreements. This helps decide if an alert about an application is actually a big deal or just a blip. It’s like having a research assistant who can quickly pull up all the related documents you need to make a quick, informed decision. This kind of tech is starting to show up in various incident management platforms.
Agentic AI For Autonomous Incident Response
Taking it a step further, we have agentic AI. This is where you have multiple AI agents, each with a specific job. One agent might be really good at spotting critical threats and flagging them immediately. Another might be responsible for taking those high-priority alerts and routing them to the right team, even including all the necessary documentation and analysis. It’s like having a specialized team where each member knows exactly what they’re good at and works together to handle incidents more smoothly. This approach aims to automate more of the investigation process, freeing up human analysts for more complex tasks.
The goal here isn’t just to automate tasks, but to fundamentally change how security operations work. By intelligently prioritizing and contextualizing alerts, these AI frameworks help teams move from a reactive stance to a more proactive one, reducing the cognitive load on analysts and improving overall security posture.
The Role Of AI In Reducing Log Ingestion Costs
Look, nobody likes paying more than they have to, right? And when it comes to security logs, the costs can really pile up. We’re talking about massive amounts of data flowing in constantly, and if you’re not careful, you end up paying to store and process a whole lot of noise. That’s where AI starts to look pretty good.
Filtering Irrelevant Logs Before Ingestion
Think about it: not every single log entry is a smoking gun. Most of it is just routine operational chatter. Traditional systems often just slurp up everything, and then you’re left sifting through it. AI can step in before the data even hits your main storage. It can learn what’s important for security and what’s just background noise. This means you’re not paying to ingest and store data that’s unlikely to ever be useful for threat detection. It’s like having a really smart bouncer at the door, only letting in the important guests.
- Intelligent Filtering: AI models can be trained to identify and discard logs that don’t align with known threat patterns or your specific security policies.
- Contextual Relevance: It goes beyond simple keywords, understanding the context of log entries to determine their potential security value.
- Adaptive Learning: The system gets better over time, learning your environment’s unique traffic patterns to refine what gets filtered.
The sheer volume of data generated by modern IT environments is staggering. Without intelligent pre-filtering, organizations are essentially paying a premium for data that offers little to no security insight, leading to inflated operational expenses and increased alert fatigue.
Reducing Storage And Processing Expenses
So, if you’re not ingesting as much data, that naturally means less storage space is needed. Less data also means your processing power isn’t being chewed up by irrelevant information. This translates directly into lower bills for cloud storage, compute resources, and any other infrastructure tied to handling your log data. It’s a pretty straightforward equation: less data in, less cost out. This is especially important as log volumes continue to grow year over year. For example, tools like Dynatrace can help with precise cost allocation for logs, showing you exactly where those expenses are coming from cost allocation for logs.
Improving Security Operations Efficiency
When your AI is helping to clean up the data before it gets to your analysts, everyone benefits. Your security team spends less time wading through irrelevant alerts and more time investigating actual potential threats. This means faster response times when something serious happens, and a more focused, less stressed team. It’s not just about saving money; it’s about making your security operations smarter and more effective. You get better visibility without the overwhelming noise, which is a win-win.
AI Log Analysis And Regulatory Compliance
Keeping up with regulations is a headache, right? Especially when your security team is drowning in alerts. It turns out, alert fatigue doesn’t just make analysts miserable; it can actually cause you to miss critical deadlines for reporting security incidents. Think about it: if your team is spending hours sifting through low-priority or false alarms, they’re not going to spot a real breach quickly. This delay can push you past the reporting windows set by rules like GDPR or the NIS2 Directive. Missing these deadlines isn’t just a slap on the wrist; it can lead to hefty fines and even personal liability for executives.
Avoiding Delays Beyond Reporting Windows
Many regulations, like the EU’s GDPR and the NIS2 Directive, have strict timelines for reporting data breaches. For instance, GDPR requires notification within 72 hours. If your security operations center (SOC) is bogged down by alert fatigue, the actual detection and confirmation of a breach can take much longer. This means you might not even realize a breach has occurred until after the reporting window has slammed shut. AI-powered log analysis tools can help by automatically correlating events and prioritizing alerts, cutting down the time it takes to identify genuine threats. This allows your team to act fast and meet those tight regulatory schedules. Tools are emerging that can help streamline these processes, making compliance more manageable.
Mitigating Regulatory Penalties And Liability
When alert fatigue leads to missed reporting deadlines, the consequences can be severe. Fines can reach millions of Euros or a significant percentage of global turnover, as seen with GDPR. Beyond financial penalties, there’s the risk of personal liability for board members and executives. This is a serious concern that can impact talent retention and company reputation. By using AI to improve alert triage and reduce the noise, organizations can significantly lower the risk of these penalties. It’s about getting ahead of the problem before it becomes a costly mistake.
Ensuring Timely Incident Notification
The core issue is that alert fatigue directly impacts your Mean Time To Detect (MTTD), which in turn affects your Mean Time To Notify (MTTN). AI log analysis offers a way to break this cycle. By intelligently filtering out noise and highlighting genuine threats, AI helps security teams identify incidents faster. This means you can initiate the notification process within the required timeframes, avoiding the penalties and reputational damage associated with late reporting. It’s a proactive approach to compliance, using technology to manage the overwhelming data flow and focus on what truly matters. This shift is vital for maintaining trust and operational integrity in today’s complex threat landscape.
The pressure to comply with evolving regulations is immense. When combined with the sheer volume of security data, alert fatigue becomes a significant compliance risk. AI offers a path to manage this complexity, not by adding more tools, but by making the existing ones smarter and more effective at surfacing real threats within the required timeframes.
Case Studies In Alert Fatigue Impact
Alert fatigue isn’t just an abstract risk for security teams—it can create real consequences when too many alerts swamp analysts and critical threats slip by. Let’s walk through a few standout examples that show exactly what can go wrong when notification overload takes over. These cases underline how tricky it is to separate real issues from hundreds or thousands of daily warnings.
Missed Alerts Leading To Major Data Breaches
The story here is unfortunately common: a critical alert comes through but disappears in the constant flood of notifications. When teams get overwhelmed, it’s easy for an important signal to get lost. One technology company managed to reduce their monthly security alerts from over 700 million down to just 18 actionable ones—seriously—to help analysts focus only on what mattered, as explored in this case study demonstrating real improvement.
The Equifax Breach And Patch Alert Failures
In 2017, Equifax received a security alert about a major software vulnerability (CVE-2017-5638). The problem? The alert joined a backlog already swamped with other notifications, and the patch wasn’t applied in time. The cost: 147 million customer records exposed and hundreds of millions in related expenses. This wasn’t a failure to detect, but a failure to act because the important alert got buried.
Insider Threats Undetected Due To Fatigue
Insider threats often produce behavioral anomaly alerts—think employees performing odd actions on internal systems. These warnings are naturally noisy because normal and suspicious activities can look similar. When teams ignore these due to fatigue, real problems slip through. Average annual losses tied to insider risks have reached $17.4 million. Here’s what often goes wrong:
- Analysts ignore repeated anomaly alerts, writing them off as false alarms
- Actual misuse of credentials or data theft isn’t caught in time
- Organizations discover insider issues only after major damage has been done
Fatigue isn’t something teams can just power through. If patterns of alert overload continue, the door stays open for attackers—inside and out—who are counting on analysts missing something important.
| Case | Missed Alert Type | Consequence |
|---|---|---|
| Technology Firm | Volume Overload | 700M alerts trimmed to 18 actions |
| Equifax (2017) | Patch Notification | 147M records breached |
| Insider Threat Cases | Behavioral Anomalies | $17.4M average annual losses |
Sometimes, the solution isn’t more alarms, but better filtering, fewer false positives, and easier ways for analysts to spot what actually needs their attention.
Measuring And Quantifying Alert Fatigue
Figuring out just how much alert fatigue is affecting your team isn’t always straightforward. Most analysts have their own hunches, like noticing when it takes longer to get through alerts or seeing more of them left untouched. But the real power comes from actually tracking measurable data, so you know where things stand now and if anything gets better over time.
Tracking False Positive Rates And Triage Time
If almost half your alerts end up being false positives, you’re not alone—this is a common pain point. You can start by logging the percentage of alerts closed as non-issues and the average speed it takes to review each alert. Over several weeks, watch those numbers:
| Metric | What It Means | Example Value |
|---|---|---|
| False Positive Rate | % of alerts with no real threat | 46% |
| Mean Triage Time | Avg time spent per alert | 70 min |
| Time-To-First-Action | Delay before alert is opened | 56 min |
If either the false positive rate or triage time climbs, you’ve got a problem worth fixing.
Monitoring Uninvestigated Alert Percentages
Uninvestigated alerts are a direct signal of analyst overload. Every SOC team should know what fraction of their total alerts never get a look. If the backlog keeps growing, it’s likely time to pause and rethink the entire strategy.
- List out the total number of alerts generated each week
- Track how many are left uninvestigated at week’s end
- Compare those percentages each month and note any trends
A rising tally of ignored alerts means important things are slipping through the cracks—maybe even threats that should have been stopped.
Establishing Baseline Metrics For Improvement
You can’t fix what you can’t measure. Pick a one- or two-month «quiet period» before rolling out any new tools or process changes, and capture the core metrics:
- Set a baseline for false positive rate, mean triage time, and uninvestigated alerts.
- Update these figures every month.
- Compare against industry averages to see where you fit in.
Sometimes, the most eye-opening thing is just seeing those numbers stacked up in black and white. What feels like a small issue day-to-day can add up to hundreds of hours lost, and maybe even real-world security incidents.
Remember, the metrics you track aren’t just numbers—they’re a window into how much stress your team is under and where you might need to take action. By watching these trends closely, you’re set up to spot alert fatigue before it quietly gets worse and drags your whole security operation down.
The Future Of Security Operations With AI
Shift Towards Signal-First Detection
For a long time, security teams just reacted to whatever alerts came their way. Most of these were noise. Now, AI is moving us toward a signal-first approach, shifting focus from sheer numbers of alerts to the quality of signals that actually matter. What does that mean? Basically, the system tries to push forward only the most relevant threats. Here’s what this looks like in real SOCs:
- Skilled analysts spend less time sifting through endless false positives.
- Correlated alerts help teams recognize patterns, making it easier to spot real incidents.
- Unimportant alerts are filtered out before reaching anyone’s desk.
If you’re curious about how organizations are transforming their strategies, check out how teams are building proactive models with artificial intelligence in their security operations centers (revolutionizing Global Security Operations Centers).
Agentic AI SOCs As The Dominant Paradigm
Folks in security used to rely on slow, manual workflows and siloed tools. But with agentic AI security operations centers (SOCs), automation and smart agents handle a growing share of the workload. Here’s what’s changing:
- AI agents automate routine investigations and follow-up.
- Alert correlation happens across all tools, reducing console sprawl.
- Analysts step in mostly for cases needing experience or tricky judgment.
Take a quick look at this table to see the shift:
| Function | Traditional SOC | Agentic AI SOC |
|---|---|---|
| Alert Review | Manual, high volume | Automated, prioritized |
| Triage Levels | Human tiers (1/2/3) | AI handles tier 1 |
| Analyst Focus | Firefighting | Investigation, strategy |
| Response Time | Hours to days | Minutes |
And as new AI tools grow more flexible, they start to act more like smart teammates than just fancy filters. If you’re thinking of transitioning, some advice from security leaders is to focus on solutions that truly amplify the team, not just replace jobs (genuinely enhance the capabilities of human analysts).
Proactive Security Operations And Reduced Cognitive Load
Instead of waiting for an alert to show up, AI-driven SOCs are starting to hunt for problems proactively—shutting down threats before they get big. Here’s how this helps:
- Reduces burnout for analysts by automating repetitive tasks.
- Improves response times, since detection and initial triage are handled by AI.
- Makes it reasonable to cover more systems and cloud services without hiring an army.
Teams shifting to AI-based workflow are finding their days a bit more manageable—less detective work, more time to focus on what matters most.
A lot of talk is about new AI products, but the real future is building a data architecture that’s ready for these changes. With the move toward more autonomous incident handling, good data quality is just as important as smart software.
In the end, the future of security ops isn’t just less noise—it’s a smarter, calmer team that can handle whatever comes next.
Moving Forward: Taming the Alert Beast
So, we’ve talked a lot about how too many alerts can really mess with your security team, making them miss important stuff and just generally burning them out. It’s like trying to hear a whisper in a rock concert – nearly impossible. But the good news is, we’re not stuck with this problem. Tools that use AI are changing the game. They’re getting smarter at figuring out what’s actually a threat and what’s just noise. This means your team can stop drowning in notifications and start focusing on the real dangers. It’s not about getting rid of alerts entirely, but about making sure the ones you get are the ones that matter, helping your security operations run smoother and keeping your organization safer.
Frequently Asked Questions
What is alert fatigue in cybersecurity?
Alert fatigue happens when security teams get too many alerts, especially from different tools. Over time, they start to ignore or miss important warnings because they’re overwhelmed by the noise.
How do I know if my team is suffering from alert fatigue?
You might notice that more alerts are left unchecked, it takes longer to review them, fewer alerts turn into real incidents, and team members may leave their jobs more often. Tracking these signs each month can help you spot alert fatigue early.
Why do security teams get so many false alerts?
False alerts often come from poorly set rules, duplicate alerts from too many tools, or logs that aren’t filtered well. When tools aren’t tuned, they can send out lots of warnings for harmless activity.
How can AI help reduce alert fatigue?
AI can group related alerts together, figure out which ones are most risky, and even handle basic investigations automatically. This means analysts only see the most important alerts and spend less time on the rest.
What are some quick ways to lower alert fatigue?
Start by turning off or fixing noisy rules, setting better alert limits, and combining duplicate alerts. These steps can make a big difference in just a month.
Can AI help save money on log storage and processing?
Yes. AI can filter out logs that aren’t useful before they’re stored or processed. This cuts down on storage costs and also means fewer pointless alerts for your team.
Does alert fatigue affect how fast we detect real threats?
Definitely. When analysts are overloaded, it takes longer to spot and respond to real attacks. This can lead to bigger security breaches and more damage to the business.
Is alert fatigue a problem for regulatory compliance?
Yes. If alert fatigue slows down your response to incidents, you might miss required reporting deadlines. This can lead to fines or other penalties from regulators.